 By

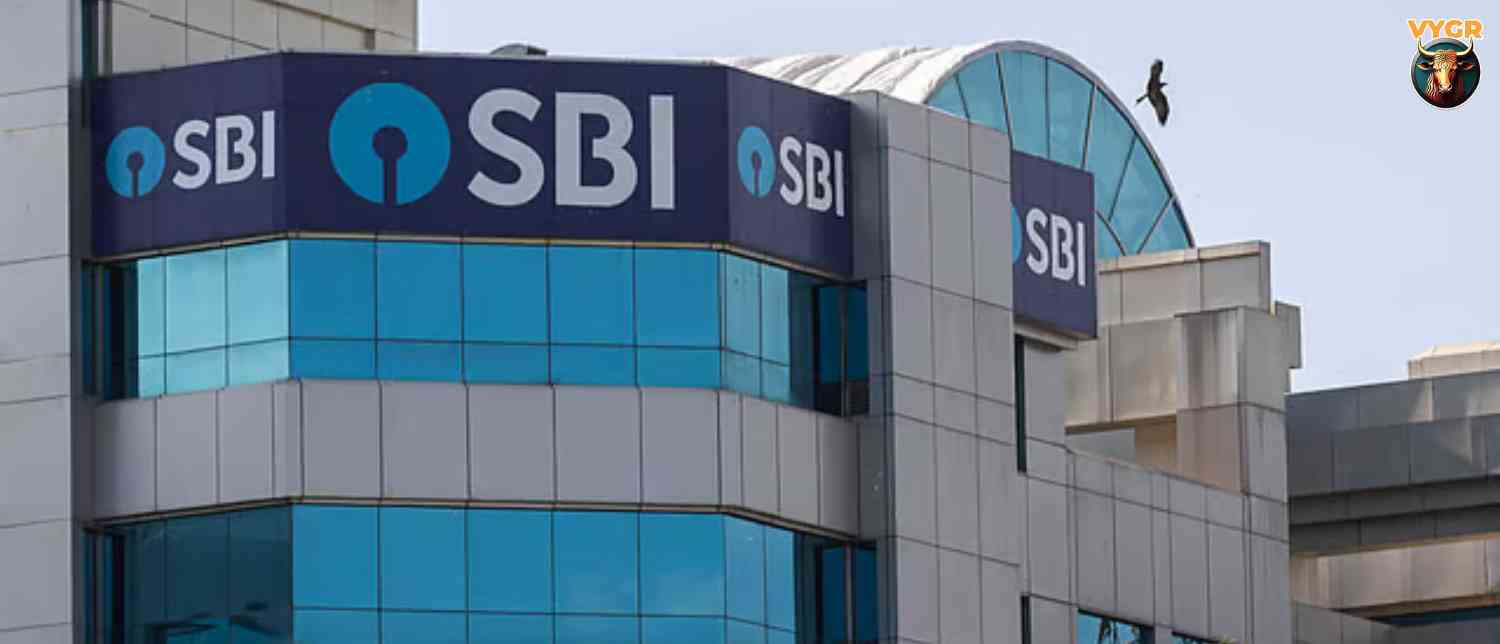
The State Bank of India (SBI), the country’s largest lender, has told investors it was hit by a cyberattack that led to the personal details of 3,897 customers being exposed on the dark web.
The bank made the disclosure in a regulatory filing on Wednesday. It said a preliminary assessment found that the leaked information included customer names, mobile numbers, dates of birth, email addresses and residential addresses, along with customer identifiers and certain loan-related records.
What SBI says
The bank said it has engaged an independent cybersecurity agency to carry out a comprehensive assessment of the nature and extent of the leak. It also said the incident is not expected to have any material impact on its core business operations, financial performance or business continuity.
That second point matters. The attack, as described, concerns data that has been exposed and not an outage of banking services. SBI has not suggested that customer funds, its core banking systems or its digital channels were disrupted.
What we know, and what we don’t
The facts SBI has put on record are narrow. Several important questions have not been answered in the filing or in the reports I reviewed:
- How the data was obtained. The bank has not said whether the records came from its own systems, from a third-party vendor or from another source.
- Who is responsible. No group has been named, and I did not find any claim of responsibility.
- When it happened. The date of the intrusion and the date the data appeared on the dark web have not been given.
- Whether other data is involved. The bank’s preliminary list does not mention account numbers, passwords or PINs, but the investigation is continuing, and the list may change.
- Which customers. The bank has not said which products or segments the 3,897 customers belong to, beyond the reference to loan records.
The independent assessment is meant to settle these questions, and the bank has not said when it expects results.
Putting the number in context
The figure is small against SBI’s size. The lender is widely reported to serve more than 50 crore customers, so 3,897 records are a tiny fraction of its base. But the number does not tell the whole story. Personal details such as a phone number, date of birth, home address and loan information are exactly what fraudsters use to make scam calls and phishing messages sound credible, and a smaller group of well-profiled victims can be easier to target than a large anonymous one.
The wider backdrop
The disclosure comes at a time of heightened regulatory focus on cybersecurity in Indian finance. The Reserve Bank of India has been pushing lenders to strengthen their security frameworks in recent years as threats to financial institutions have grown. Companies in India must report cyber incidents to the national computer emergency response team, CERT-In, within six hours of noticing them, and listed companies have to inform stock exchanges of material events. SBI’s filing reflects the second of those obligations. The bank has not said whether it has also informed CERT-In or the RBI, though such reporting is normally expected.
Breaches at large institutions have become a familiar story in India, and elsewhere. The usual pattern is a quiet period, followed by the discovery of stolen data on a criminal forum or a dark web marketplace. No link between this incident and any earlier breach has been reported.
What SBI customers can do
The bank has not issued specific advice to customers in the reports I reviewed, but standard precautions apply.
- Treat unexpected calls and messages with suspicion. Fraudsters with your name, address or loan details can sound convincing. Banks do not ask for your PIN, password, CVV, or one-time password.
- Don’t click links in unsolicited SMS or emails. Use the bank’s official app or website instead.
- Check your statements and alerts. Turn on SMS and email alerts for every transaction, and look for anything you don’t recognise.
- Contact the bank through official channels if you receive a suspicious call that seems to refer to your loan.
- Report fraud quickly. In India, cyber fraud can be reported on the national helpline 1930 or at cybercrime.gov.in, and acting within hours improves the chance of blocking a transaction.
What to watch
The findings of the independent investigation, any further disclosure from SBI about the scope of the data, and a response from the RBI or CERT-In are the main things to watch. If more records turn up, the number may rise.
© Copyright 2026. All Rights Reserved. Powered by Vygr Media.